
Vulnerability Assessment and Patch Management Services to Discover, Prioritize, and Remediate Risk
Scanning tells you what's exposed. CES closes it. Our Vulnerability Assessment and Patch Management service takes you from asset discovery to validated remediation with one engineering-led team accountable end to end across Windows, Linux, VMware, databases, middleware, and cloud.

Trusted to secure hybrid, multi-cloud, and legacy IT estates across regulated industries
Beyond Vulnerability Scanning: VA and PM That Closes the Gap
Most enterprises don't struggle to find vulnerabilities. They struggle to close them. Our Vulnerability Assessment and Patch Management service embeds risk-based prioritization, remediation engineering, and patch governance into every layer of your estate, closing exposure before it becomes an incident.
From asset discovery to validated remediation, we build and run vulnerability management capabilities that cut backlog, enforce ownership, and keep every platform provably patched.
Key areas we support:
- Vulnerability assessment across systems, applications, network, and cloud
- Risk-based prioritization beyond CVSS alone
- Remediation planning and infrastructure modernization
- Cross-platform patch management and governance
- Continuous Vulnerability Management with ongoing monitoring and compliance reporting
Backed by a dedicated engineering team, our VA and PM model delivers faster remediation, stronger compliance posture, and continuously reduced exposure.
Our Vulnerability Assessment and Patch Management Service Offerings

Vulnerability Assessment: Deep Technical Coverage
We deliver Vulnerability Assessment as a Service through authenticated and unauthenticated scanning across systems, applications, networks, and cloud environments.
- Asset discovery across on-premises, hybrid, and cloud
- Authenticated and unauthenticated scanning
- OS, application, and database vulnerability identification
- Network device and cloud infrastructure assessment
- End-of-support and end-of-life identification

Risk-Based Vulnerability Prioritization
We prioritize vulnerabilities using exploitability, business context, exposure, threat intelligence, and compensating controls to focus remediation on the highest risks.
- Multi-factor risk scoring beyond CVSS
- Exploitability and threat intelligence correlation
- Asset criticality and business impact weighting
- Exposure and attack surface analysis
- Risk-based remediation sequencing

Vulnerability Remediation & Infrastructure Modernization
Our Vulnerability Remediation Services identify and implement the most effective path, from patching and upgrades to modernization, and validate the outcome.
- Root cause analysis for prioritized findings
- Patch, upgrade, or modernization decisioning
- Dependency and compatibility analysis
- Change planning and coordinated implementation
- Post-remediation validation

Cross-Platform Patch Management
One governance model for Enterprise Patch Management across operating systems, infrastructure, applications, databases, and cloud workloads.
- OS patching across Windows, Linux, Unix, macOS
- Infrastructure patching across VMware, Hyper-V, physical servers
- Application and database patch deployment
- Cloud workload patching across Azure, AWS, and GCP
- Remote endpoint patch coverage

Governance, Compliance & Executive Reporting
As part of our Managed Patch Management program, we track patch compliance, remediation performance, vulnerability trends, and SLA adherence with reporting that supports security, audit, and executive stakeholders.
- Executive dashboards for exposure and posture trends
- Patch compliance and SLA tracking
- Mean Time to Remediate (MTTR) and vulnerability aging metrics
- Exception governance and audit-ready reporting
- Compliance alignment for regulated environments
What We Find,
We Finish
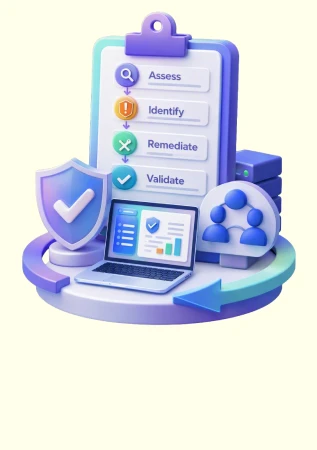
Dedicated Engineering, Not Ticket Queues
One accountable team manages assessment through remediation. No vendor hand-offs, no siloed ownership, and no findings left unresolved.
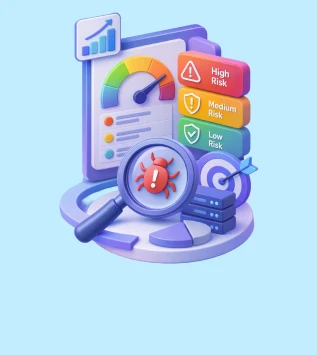
Risk-Based, Not "Patch Everything"
We prioritize remediation by exploitability, business impact, and exposure, so effort is focused on reducing risk, not clearing the longest list.
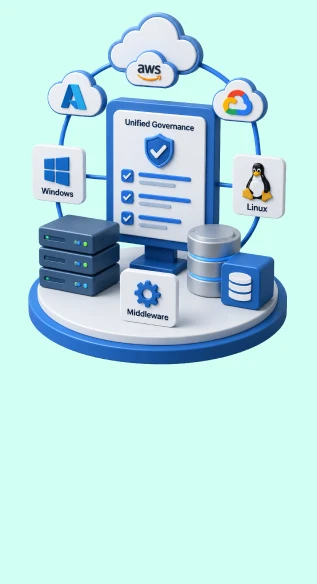
Cross-Platform and Hybrid Cloud Native
Windows, Linux, virtual infrastructure, databases, middleware, and multi-cloud workloads managed under a single governance model.
Automation-First, 24×7 Support
From automated patch deployment to governed remediation workflows, we help drive automation maturity, backed by round-the-clock operational support.
Our End-to-End Vulnerability Remediation Approach
CES runs vulnerability assessment and patch management as one continuous lifecycle: from discovery to governance, not a set of disconnected engagements.
Assess & Analyze
Discover assets and vulnerabilities across the full estate, then score severity, exploitability, and exposure.
- Full asset and vulnerability discovery
- Authenticated and unauthenticated scanning
- Severity, exploitability, and exposure analysis
- Configuration and security baseline deviation checks
Prioritize & Plan
Sequence remediation by real business risk and build the specific patch, upgrade, or modernization plan for each finding.
- Risk-based remediation ordering
- Patch and remediation plan development
- Dependency and compatibility analysis
- Change window and approval planning
Remediate & Validate
Deploy patches, fixes, and upgrades, then verify the vulnerability has been effectively remediated.
- Patch, fix, and upgrade deployment
- Infrastructure and application modernization
- Post-remediation verification
- Compensating controls where remediation isn't immediately possible
Govern & Report
Deliver compliance views and executive dashboards that track exposure trends, SLA adherence, and audit readiness continuously.
- Executive and compliance dashboards
- Patch compliance and SLA tracking
- Vulnerability aging and MTTR reporting
- Exception governance and audit trail
Why Vulnerability Assessment and Patch Management Matters
- Reduce the vulnerability backlog instead of just measuring it
- Cut Mean Time to Remediate (MTTR) with a team that owns remediation, not just findings
- Close compliance gaps across key regulatory and security frameworks
- Modernize unsupported and end-of-life systems before they become security risks
- Replace fragmented, manual patching with governed, automated processes
- Gain continuous executive visibility into exposure, risk, and security posture trends
FAQs
Vulnerability Assessment & Patch Management
Vulnerability assessment is the scanning and identification step. It tells you what is exposed.
Vulnerability management services cover the ongoing lifecycle: assessing, prioritizing, remediating, and monitoring continuously.
CES delivers the full lifecycle, not just the scan.
CVSS measures theoretical severity, not real-world risk. A critical CVSS finding on an isolated, non-internet-facing asset may matter less than a high finding on an internet-exposed system with an active exploit in the wild. We combine CVSS with exploitability, asset criticality, business impact, internet exposure, and threat intelligence to prioritize what needs attention first.
Yes. Cross-platform patch management is core to the service, covering Windows Server and desktop, Linux/Unix, macOS, VMware/Hyper-V, physical servers, databases, middleware, and workloads across Azure, AWS, and GCP, under one governance model.
For every finding, we determine whether it can be patched, needs to be upgraded, or requires modernization or replacement because the platform is unsupported. Where none of those are immediately possible, we implement compensating controls and document the risk treatment rather than leaving it unaddressed.
Our vulnerability intelligence feeds run continuously, not on a schedule. When a zero-day is disclosed, we assess exposure against your specific asset inventory, prioritize based on real exploitability and exposure, and move directly into patch or mitigation planning.
Yes. We track patch compliance, open critical vulnerabilities, remediation SLA adherence, and exception status, and deliver executive and audit-ready reporting aligned to the compliance frameworks your organization is measured against.
We run a best-of-breed, vendor-agnostic stack, including Tenable, Qualys, and Rapid7 for vulnerability management; Microsoft Intune/SCCM, BigFix, Tanium, Automox, and Ivanti for endpoint and patch; and native cloud tools like Defender for Cloud, AWS Security Hub/Inspector, and Google Security Command Center, matched to your existing environment.
It means we move remediation up the automation maturity curve deliberately: from manual, ticket-driven fixes, to scripted patch deployment with compliance checks, to governed, self-healing remediation with guardrails. We don't leave every patch cycle as a manual exercise indefinitely.
Want deeper insight into how risk-based prioritization or cross-platform patch management work in your environment?
Get expert answers on prioritization, remediation, patch governance, compliance, automation, and more.
VAS Knowledge Basestrategic client partner

Take the Next Step
We don't just patch. We reduce technology risk. Let's assess your current exposure and build a prioritized remediation roadmap.
Contact us today